Infographic
The Cost of Internally Patching
Explore the often-overlooked costs and risks associated with in-house patch management.


Right Click Tools
Enhance security, compliance, and efficiency across enterprise environments
Right Click Tools Patching
Right Click Tools Insights
Right Click Tools Privileged Access
Free Tool Download
Pricing

Application Workspace
The game-changing, end-to-end application management platform
Request a Demo
Pricing
Use Case
Function
Learn
Engage
Product
Who We Are
Partners
Login
In December 2024, the Clop ransomware gang—the same group behind the MOVEit breaches—exploited a zero-day in Cleo’s managed file-transfer software (CVE-2024-50623). More than 200 organizations were posted to Clop’s leak site within a single month. Cleo’s first patch was incomplete and bypassed by attackers; an effective fix didn’t arrive until January 2025.
BleepingComputer — “Clop ransomware claims responsibility for Cleo data theft attacks” (Dec 2024).
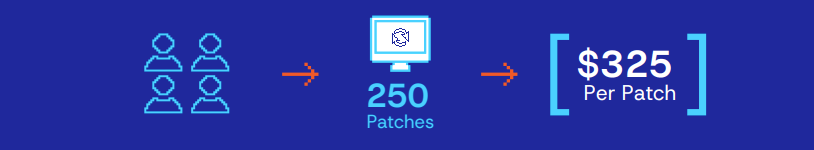
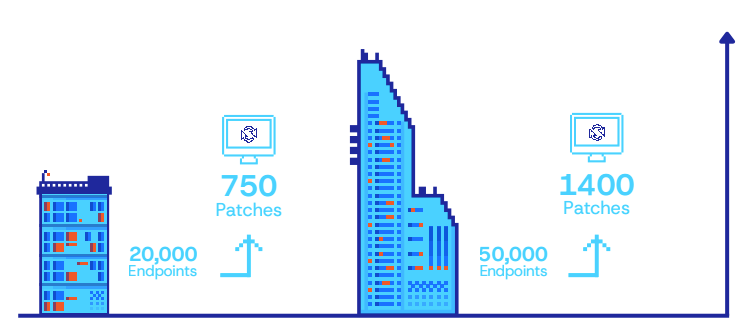
*These figures are conservative estimates based on customer feedback used to illustrate the scaling of resources and costs. Many teams require more resources and patch more applications at the endpoint counts listed.
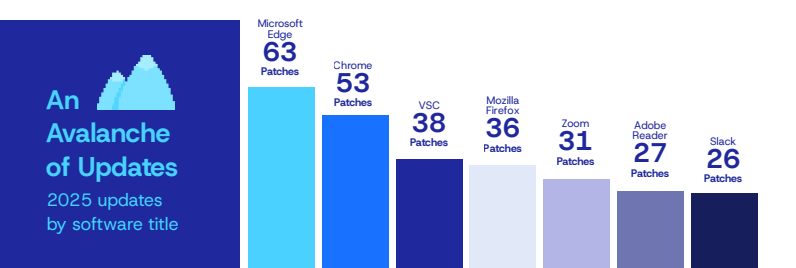
The in-house patching process is a relentless cycle of pilot testing, preproduction, and production patching—often disrupted by new patches before the previous ones are fully deployed. This ceaseless loop runs 24/7/365. Holidays or weekends? Forget them! Zero-day patches don’t care about time off, as underscored by Chrome’s relentless stream of emergency fixes. By June 2026, Google had already shipped its fifth actively-exploited Chrome zero-day patch of the year (CVE-2026-11645).
Verizon’s 2025 Data Breach Investigations Report found the human element involved in roughly 60% of breaches, while exploitation of vulnerabilities as an initial attack vector jumped 34% year-overyear. (Verizon 2025 DBIR)
Traditional patch management is inefficient and costly. Automated patching streamlines updates, reduces risks, and frees IT for strategic growth initiatives.